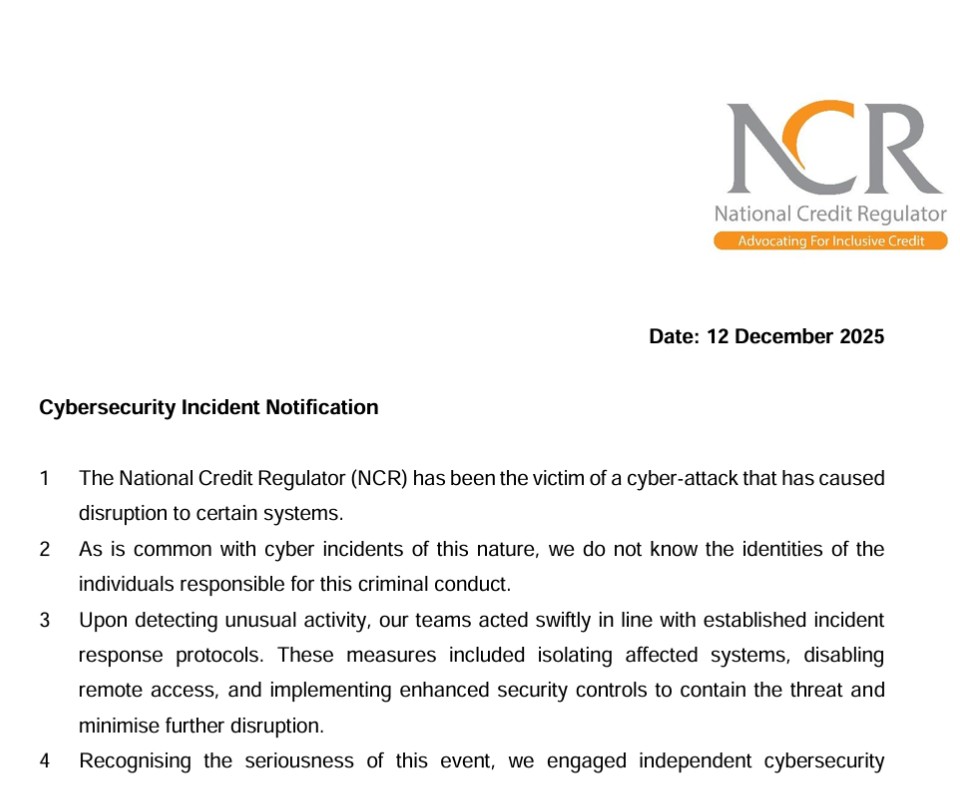
NEWS: NCR Publish That They Have Been Hacked
The NCR have an extensive database of all registered Debt Counsellors, Credit Providers, Credit Bureaus and Payment Distribution Agents.
This public database is easily found on the website and is designed to provide visibility and clarity for any consumers wanting to check that someone they are dealing with (for a loan or debt counselling) is really registered with the NCR.
The NCR also has another, more extensive database of all consumers who have ever asked a Debt Counsellor for assistance or professional advice. Debt Counsellors regularly update this database (Called NCR Debt Help).
The NCR also collect and compile information from credit bureaus and credit providers.
There have recently been several concerned parties within the industry who were worried that the NCR site may be vulnerable and that it may be possible to find information that could be considered private and confidential. In light of PoPI requirements, everyone these days worries about data security and what bad people may do if they find sensitive data.
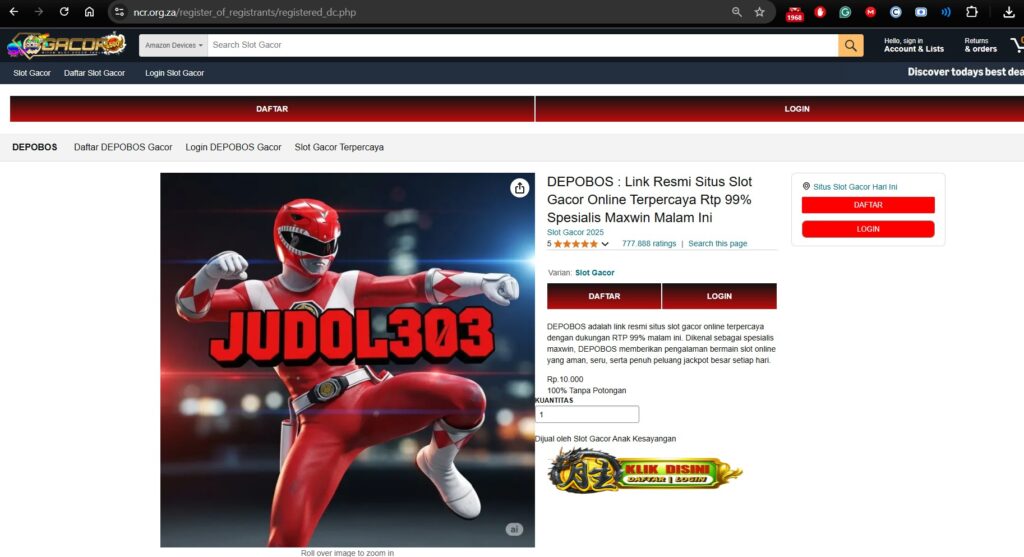
In September this year, the NCR was a victim of a website hack.
This caused the website to redirect, and Google search results to come back with weird results pointing to the Ministry of Islamic Affairs:

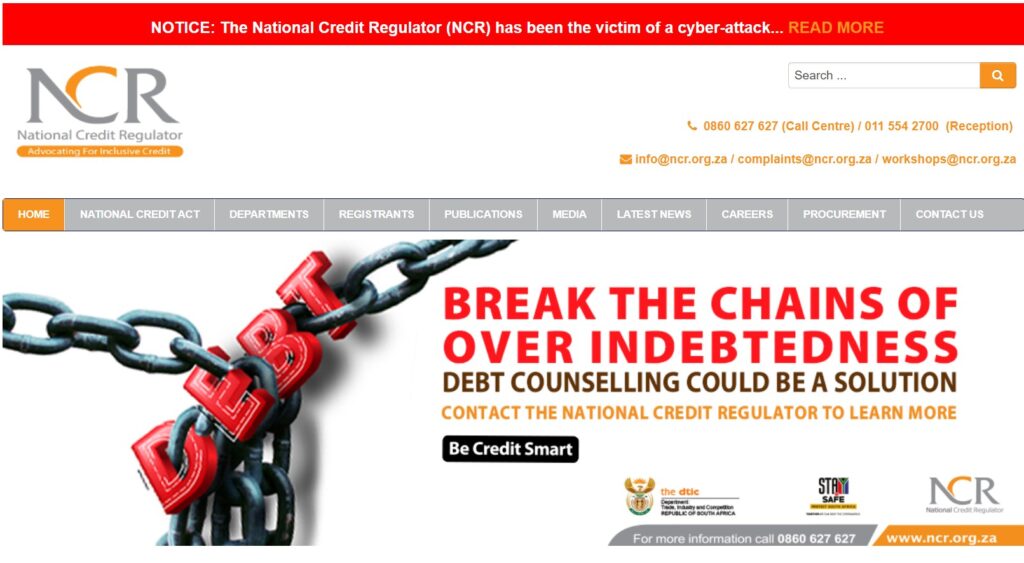
When you went to their site (www.ncr.org.za) you got this stripped down version of the website: